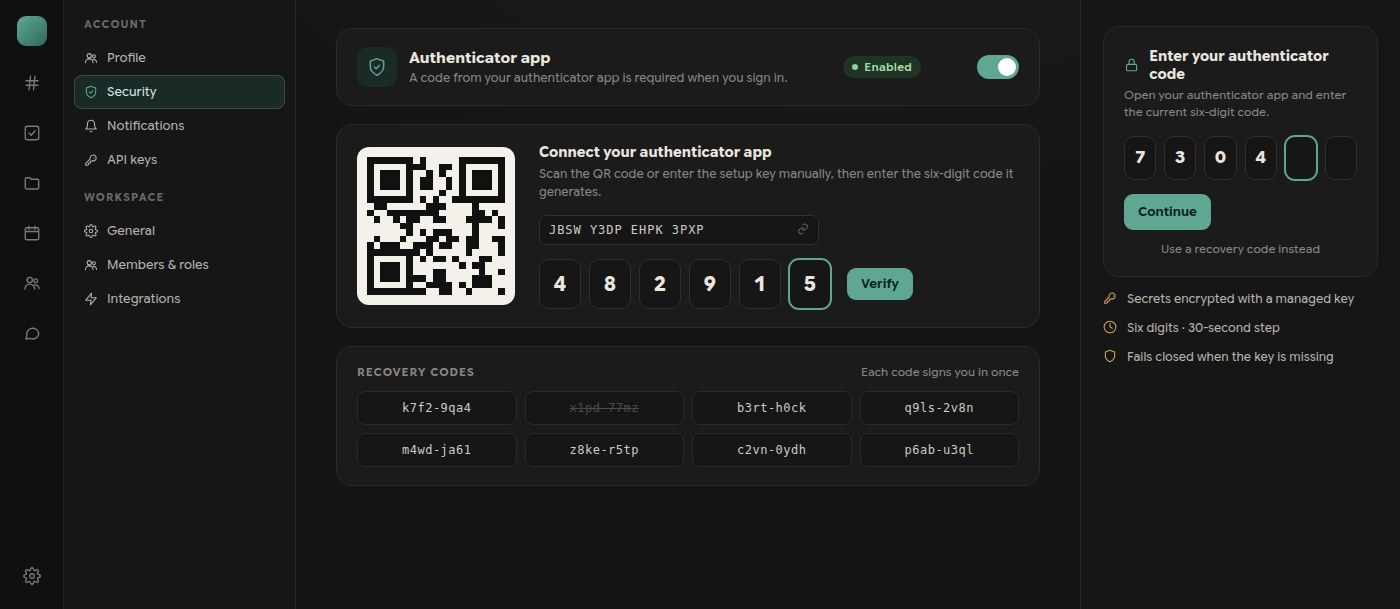
Polybase accounts can now be protected with a second factor. Enable multi-factor authentication from account security settings, scan a QR code with any authenticator app that speaks the standard six-digit, 30-second TOTP profile, and save the single-use recovery codes shown once at setup. From then on, an enrolled account must complete the second factor before a session token is issued; password, magic-link and future OAuth sign-ins remain the first factor.
The design refuses shortcuts. A password plus an email code is not accepted as a second factor for an enrolled account, replayed codes are rejected, recovery codes are stored as keyed digests and can never be read back, and validation admits only a narrow clock-skew window.
Like everything else in Polybase, MFA stays inside your deployment. On first boot the server generates a random master key and keeps it in the data directory with owner-only permissions; it encrypts TOTP secrets at rest, travels with full backups, and is never copied into images, source control or tenant exports. If the key is missing or cannot decrypt stored factors, the server fails closed rather than silently disabling protection.
- Opt-in TOTP with any standard authenticator app
- Single-use recovery codes, shown once and stored as digests
- Second factor enforced before any session token is issued
- Managed encryption key kept in your own data directory
- Fails closed if the key is missing or cannot decrypt stored factors